Outstanding Expertise
Information Security Consulting
Whether you’re establishing or expanding an information security management system, conducting a quick check, or preparing comprehensively for an audit in accordance with ISO 27001, IT-Grundschutz, KRITIS, TISAX, or Section 44 of the German Banking Act (KWG)—we have the expertise you need to bring your information security up to the optimal level of maturity.
Information Security Management System
ISMS
We can help you define an information security management system (ISMS) for your company or analyze and optimize an existing one. With an ISMS, you will be able to define, manage, monitor, maintain, and continuously improve your company’s information security.
Critical Infrastructure
KRITIS
Do you need advice on whether your company falls under the KRITIS Regulation and want to know what this means for your business? Or are you already a registered KRITIS company and need assistance with implementing or improving compliance with the requirements?
Whether it’s a GAP analysis, an in-depth KRITIS audit, communication with the BSI, training, or assistance in addressing deficiencies—we have numerous KRITIS experts and managers who will support you in all matters.
ISO 27001 Consulting
Would you like to demonstrate to your customers that you have established a high level of protection based on ISO 27001? Or are you even aiming for ISO 27001 certification? Is your ISMS aligned with ISO 27001, and do you need expert support to establish or further develop it?
We have certified and experienced ISO 27001 Lead Auditors who will support you through our information security consulting service at
and help you find the most efficient and effective path for your company.
Risk Management for Information Security
GOVERNANCE, RISK, AND COMPLIANCE
What is the most effective and efficient way to control, measure, manage, escalate, and regularly report information security risks to all necessary stakeholders?
We understand the challenges and potential solutions involved in establishing an efficient information security reporting system, interpreting legal and regulatory requirements, defining and setting up an internal control system, and balancing security benefits against risk acceptance.
When BaFin comes knocking...
§44 SPECIAL IT EXAM
We have extensive experience in preparing for, conducting, and following up on special IT audits under Section 44 of the German Banking Act (KWG), as well as in mitigating findings by the German Federal Financial Supervisory Authority (BaFin).
What is the best way to prepare for a Section 44 audit, and how does it proceed? What types of findings—and at what levels of severity—can be expected, and what consequences might these have for management?
How do you implement a comprehensive mitigation program to address the findings, including regular reporting to BaFin, and how do you find suitable (external) personnel to carry out the remediation?
From strategy and analysis through implementation and remediation to ongoing operations, we can provide you with comprehensive support using our expertise. We have already navigated and resolved all of these situations and are familiar with every potential pitfall you may encounter.
Standards & Policies
Do you need watertight policies covering all aspects of information security? Or do you need to review and optimize your company’s existing policies?
Whether it’s a “
” information security policy or guideline, the classification of information, the definition of a risk appetite, or the definition and measurement of risks and controls… We’ll help you define the guidelines that make the most sense for your organization and implement them within your company.
Especially for KRITIS operators
External ISB
It is very difficult to find qualified expertise from an experienced Information Security Officer (ISO) on the market. However, legal and regulatory requirements compel companies to either develop this expertise internally or procure it externally.
We have many years of experience as information security officers and can support you quickly, efficiently, and professionally as an externally appointed ISB. If you wish to fill this position internally, we can also assist you in finding suitable candidates for the role.
With us, you won’t get a lone wolf, but rather a team of experienced experts who work together to continuously monitor and support your company’s security.
WIDELY ESTABLISHED IN INFORMATION SECURITY
EXPERTISE
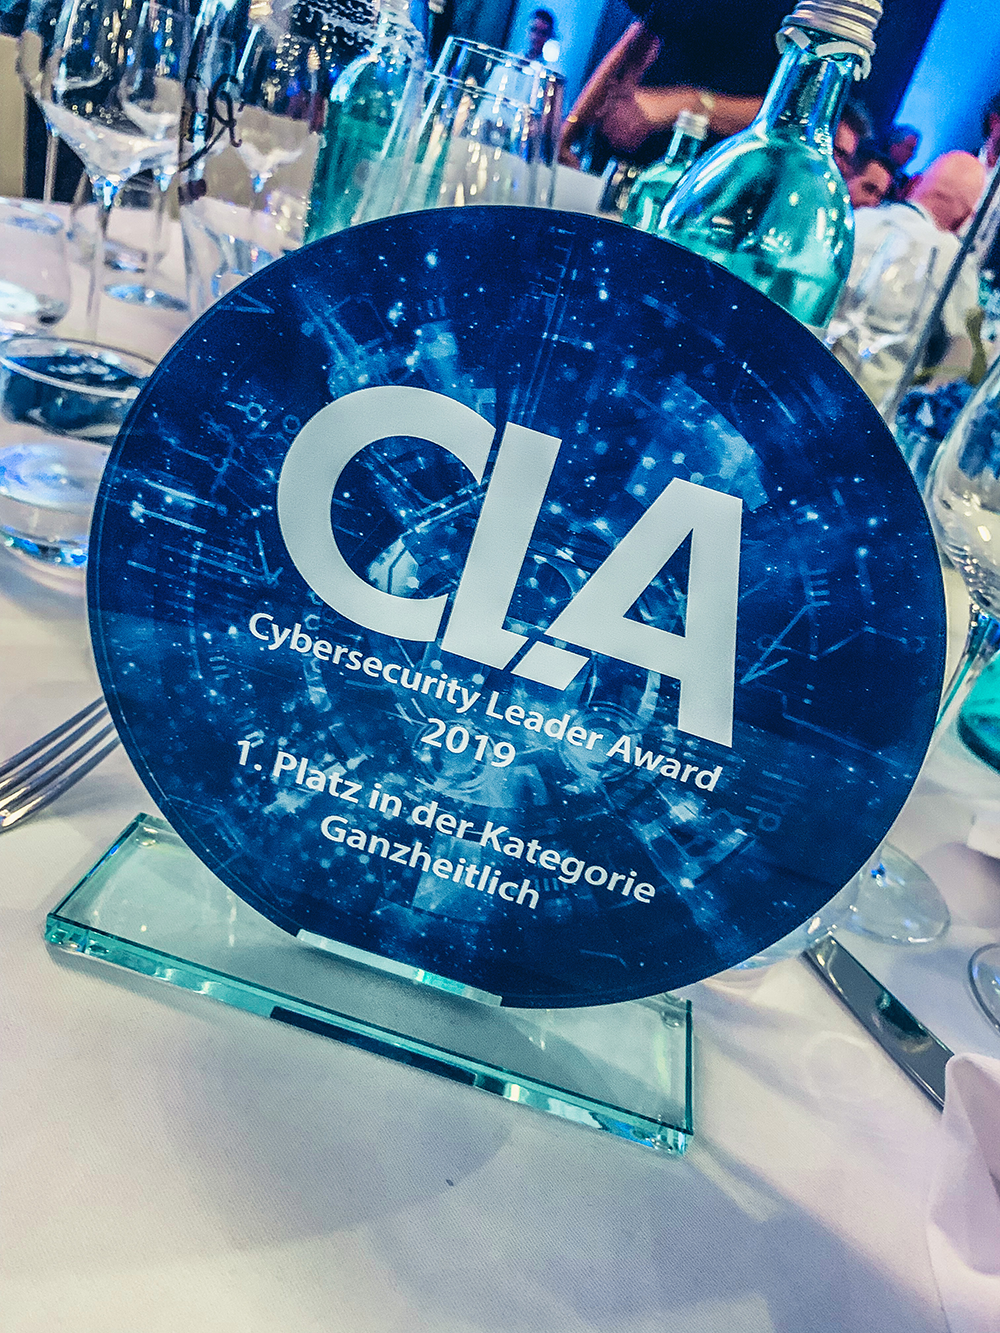
From junior risk managers to senior auditors, ISO 27001 lead auditors, and IT-Grundschutz lead auditors, all the way to long-standing, experienced, and award-winning information security officers (ISOs). Our employees cover virtually every area of information security.
We bring over 100 years of professional hands-on experience to your company.
FULL-STACK PROTECTION FOR YOUR SAP SYSTEM
SAP SECURITY CONSULTING
Are you looking to implement a new SAP system, or do you already use SAP and want to secure it (even better)?
We support you in planning, setting up, and ensuring the long-term security of your SAP systems. This includes, among other things, an SAP security strategy, manual and automated SAP security vulnerability assessments, the identification of security-related misconfigurations, detailed and targeted reporting, and regular security code analyses.
YOUR STRENGTH IS
OUR EXPERIENCE
Whether you’re a small business, a medium-sized company, or a large international corporation—whether you’re in government, manufacturing, retail, banking, the automotive industry, the energy sector, or aviation—our employees have seen (almost) it all and always find the best and most effective measures to bring and maintain your company’s information security at the desired level of maturity.
We are
Your SWAT Team
At Apollon Security, we don’t have lone wolves—only team players. You benefit from this strong team behind the scenes, both in our consulting services and in every product and service we’ve developed ourselves.
Our hiring process is very rigorous. We only hire people who share our mindset and perform at the highest level, both professionally and personally.